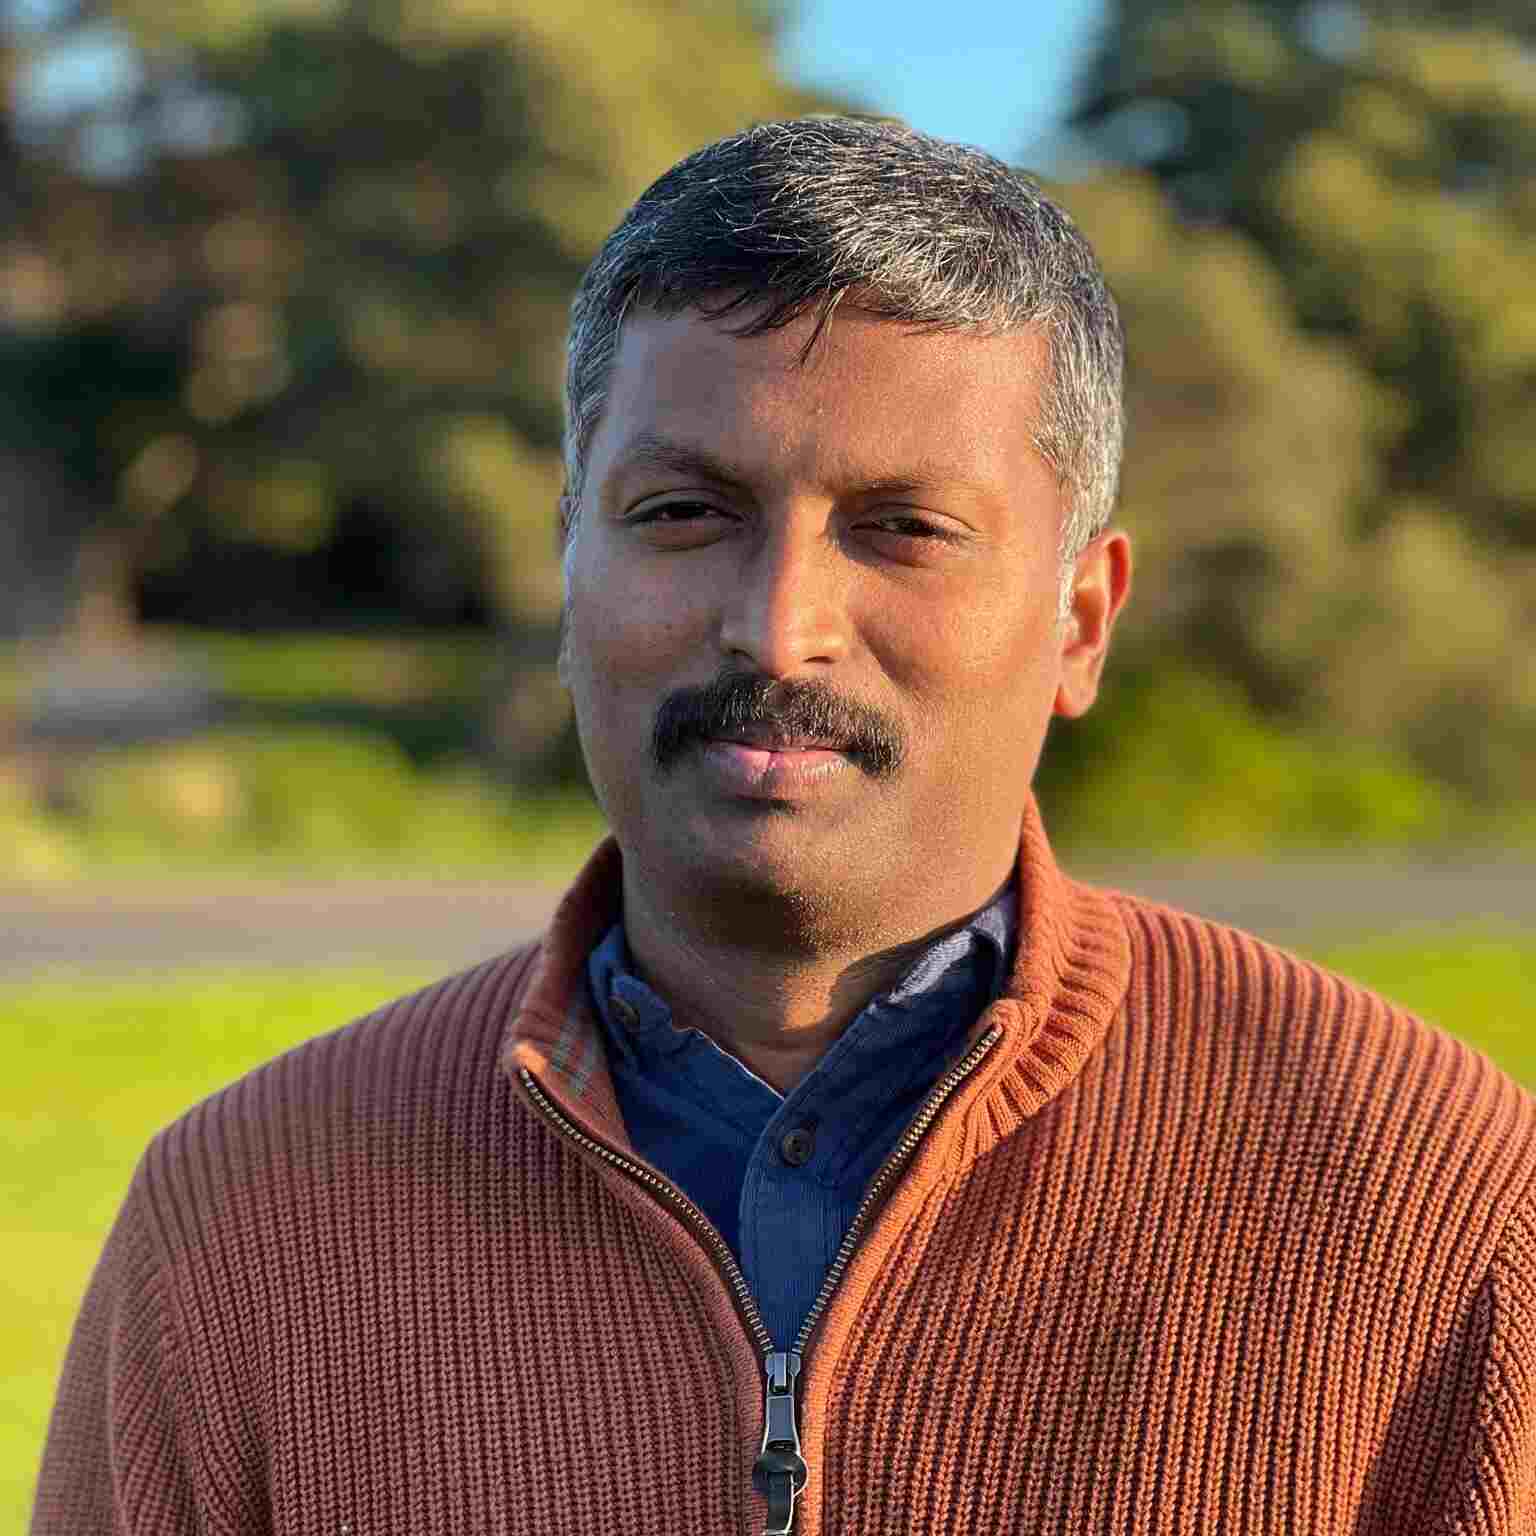
Santhoshkumar Anandakrishnan
Skyline Technology Aus Pty ltd - Melbourne

September 10, 2026 | 6:00 - 7:00 AM (UTC) Coordinated Universal Time
Ready to get started with AI and the latest technologies? Microsoft Reactor provides events, training, and community resources to help developers, entrepreneurs and startups build on AI technology and more. Join us!
September 10, 2026 | 6:00 - 7:00 AM (UTC) Coordinated Universal Time
Ready to get started with AI and the latest technologies? Microsoft Reactor provides events, training, and community resources to help developers, entrepreneurs and startups build on AI technology and more. Join us!
September 10, 2026 | 6:00 - 7:00 AM (UTC) Coordinated Universal Time
 Livestream
Topic: Security
Language: English
This session makes the case for "guardrails, not gates": governance that's built into the platform itself rather than bolted on afterward.
We'll start with Azure Policy fundamentals, including policy definitions, initiatives, and effects (Deny, Audit, DeployIfNotExists, Modify), and explore how each effect type is appropriate for different governance scenarios.
From there, we move into practical network security baselines, covering policies that:
The session then zooms out to the Cloud Adoption Framework Landing Zone model, showing how these individual policies are assembled into a coherent governance architecture and applied automatically at subscription vending time. This ensures every new subscription inherits the right guardrails from day one, rather than having security retrofitted later.
We'll also cover:
Speakers
Santhoshkumar Anandakrishnan
Skyline Technology Aus Pty ltd - Melbourne
The events below may be of interest to you as well. Be sure to visit our Reactor homepage to see all available events.
Format:
Livestream
Topic: Security
Language: English